This project is a web application for generating passwords. Its purpose is to avoid predictable choices based on names, dates, or words that are easy to associate with a person.
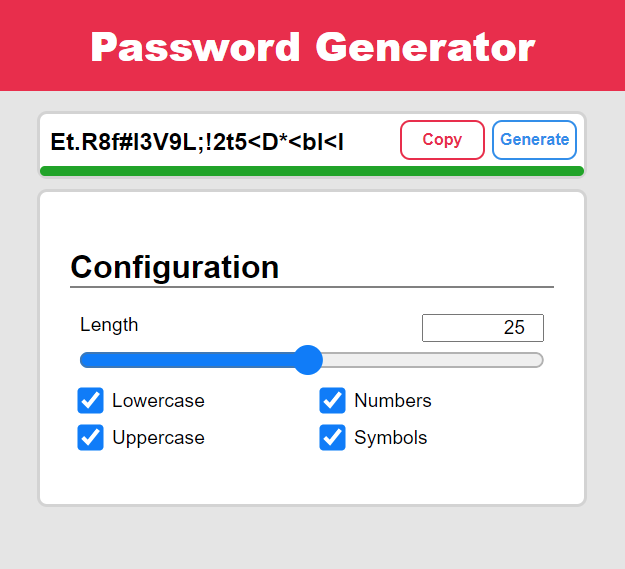
Generating a string is only part of the problem
A password’s strength depends on its length, how its characters are chosen, and whether it is reused across services. The source of randomness matters: a sequence that looks scrambled is not necessarily unpredictable.
No tool should promise passwords that are “impossible to hack”. A long password cannot, by itself, prevent phishing or a breach of the service that stores it.
Read the project with that question in mind
The demo and source code provide a way to study the interface and generation process. Before using a generator for real credentials, check its randomness source and limitations. In web applications, the browser’s cryptographic API provides crypto.getRandomValues(); Math.random() is not suitable for that purpose.
If you enjoy small development tools, take a look at Copyright O’matic too.